Before pasting client material into AI, separate two questions: what information is in this input, and what processing did the client authorize? A useful task and a private-looking chat window do not answer the second question.
This guide is for freelancers handling entrusted information. Employees should start with their workplace policy. Your project agreement and client instructions are the starting point here; a chatbot cannot interpret them into permission on your behalf.
Recognize the material before sending it
Pause for credentials or access links, unpublished figures and plans, security details, private contract terms, customer or staff information, and anything covered by confidentiality instructions. Inspect attachments as well as the visible prompt: extra pages, comments and unrelated records can be unnecessary for the task.
Confirm the exact tool and account, the purpose, the permitted data categories and any connected recipient. If the authorization is unresolved, keep the material out of that tool and ask the responsible client contact. Provider training controls and Temporary Chat settings describe how a product handles particular uses; they do not supply contractual permission.
A safer pattern question
This is a fictional teaching example, not a real client’s data or a recorded product test.
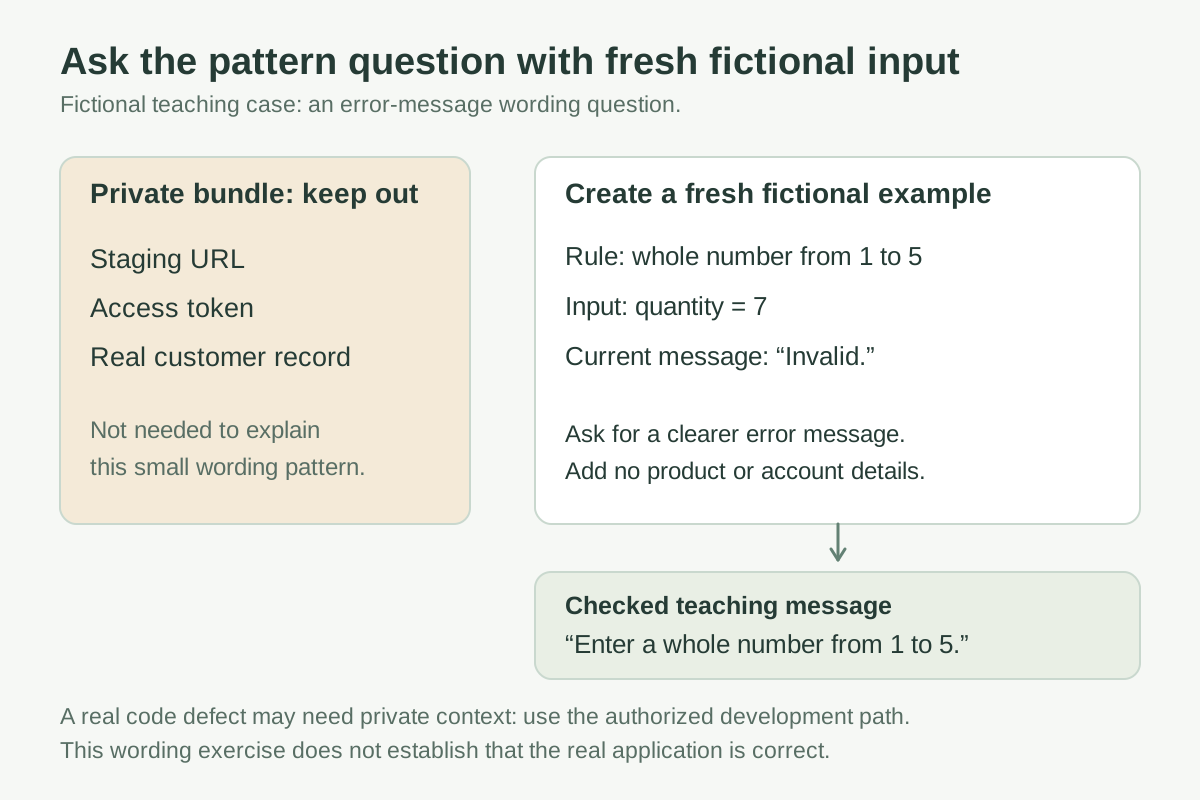
A developer wants help explaining a confusing validation error. Their original draft includes a staging URL, an access token and a real customer’s record. None is necessary to ask about the validation pattern.
Instead, create a fresh toy input:
In this fictional form, quantity must be a whole number from 1 to 5.
Input: quantity = 7.
Current message: “Invalid.”
Suggest a clearer error message. Do not add product or account details.
A checked teaching output is: “Enter a whole number from 1 to 5.” It states the provided constraint and adds no customer detail. That answers a small wording question without transmitting the client’s record. It does not prove that the real application’s validation or security is correct.
For a code defect that genuinely depends on private implementation details, use an authorized development environment or ask for the required access decision. Do not keep stripping context until an answer to a different problem looks reassuring.
Redaction is a check, not a guarantee
Removing a company name may leave a distinctive deal, role or product identifiable. Prefer a synthetic example when the task only needs structure. Where real data is necessary and authorized, send only what the purpose requires. The ICO’s data-minimisation guidance explains that principle for personal data; it does not establish that redaction made a record anonymous.
Legal roles also depend on the arrangement. The EDPB’s controller and processor guidance is a starting point for GDPR role questions, not a substitute for advice about your contract. Client approval does not by itself settle every obligation concerning other people’s information.
If the paste already happened
Stop the affected use. Through the client’s designated incident channel, record the tool, account, time and category of data involved. Avoid repeating the disclosure in a fresh chatbot or unnecessary screenshot. Contact the responsible client or security person promptly, preserve relevant evidence, and use the authorized route to revoke or rotate exposed credentials.
Let the responsible responders determine required notifications, preservation and deletion. Deleting a chat or switching off training does not establish that the transmission was undone. ENISA’s SME cybersecurity guide provides broader security and incident-planning guidance for small businesses.
Keep the paste-stop card beside your project notes. The solo client rules card records the permission decision; this stop check is what you apply to the actual material about to leave your control.