Some tools and platforms show a “Content Credentials” icon or an AI-content label on images and videos. It can look like a verdict - real or fake, trustworthy or not. It is narrower: a specific provenance assertion or platform disclosure whose exact meaning must be inspected.
What the badge is actually checking
Content Credentials is the consumer-facing name for a technical standard called C2PA (the Coalition for Content Provenance and Authenticity). When a supporting tool creates or edits a file, it can attach a signed manifest recording facts about that file’s history: what created it, what tools touched it, and what actions were declared along the way (C2PA technical explainer).
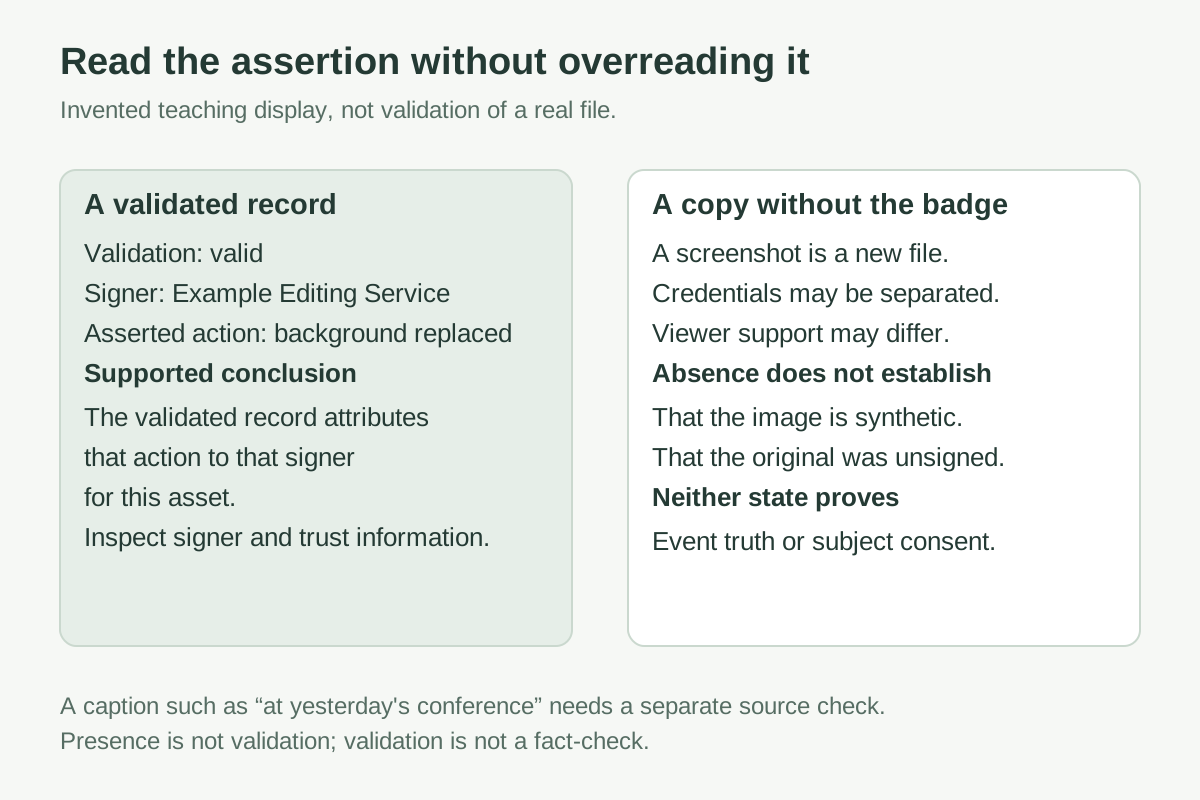
When validation succeeds, the credential binds the asset to signed assertions about its history. Inspect both that result and the signer/trust information shown by the viewer. A badge alone is not evidence that validation succeeded or that a particular person created the asset.
What it is not telling you
The badge is not a fact-check, and it does not answer several questions people often assume it does:
- It does not confirm the depicted event actually happened the way it looks.
- It does not confirm the person in the image or video consented to being shown that way.
- It does not confirm the caption or context around the file is accurate.
- It does not confirm the signer is honest - a trusted account can still sign a misleading image.
- It does not mean a file without the badge is fake. Credentials may never have been created or may have been separated from the file.
A missing badge does not establish whether provenance was never recorded, removed or unsupported by the viewer.
Do not treat a missing Content Credentials badge as suspicious on its own. C2PA is opt-in, credentials may never have been created, and later processing can remove or separate provenance data from a file.
What breaks the badge, without breaking the file
Even when a credential exists, ordinary handling can remove it before the file reaches you:
| What happens to the file | What typically happens to the credential |
|---|---|
| Screenshot or screen recording | Creates a new file that is not the original signed asset |
| Re-upload through an unaware app | Credential may be stripped during export |
| Heavy compression or format conversion | May break a credential or watermark |
| Forwarded through messaging apps | Credential may be stripped by processing |
| Copied caption onto a different file | No cryptographic link between the caption and any credential |
A genuine, originally signed photo can lose embedded credentials after a screenshot or export. Some systems can recover associated provenance using fingerprints or watermarks, called soft bindings in C2PA. Recovery depends on implementation. An absent badge leaves creation, preservation and viewer support unresolved.
Watermarks are a related but different tool
A watermark places a visible or machine-detectable signal in the content. A metadata label stores a declaration alongside it; that is a different mechanism. Either can indicate synthetic origin, but robustness depends on the implementation and transformations applied. Cropping, compression, screenshots or re-encoding may degrade or remove a signal. No detected watermark does not establish whether one was ever added or whether the file is synthetic.
Why this matters: the same gap detectors leave open
This is the direct counterpart to the detection problem covered in AI image limits, not detectors: there is no reliable, universal way to look at a file and know for certain whether it is AI-generated, edited, or genuine. Content Credentials improve the picture when they are present and intact, but they are a signed assertion from the file’s creator, not an independent verdict - and they frequently are not present at all. Use the badge as one useful input, never as the deciding factor for anything consequential.
A practical reading order
When you see a Content Credentials badge or an AI-content label, work through it in this order:
- Is the credential actually valid, according to the platform showing it (not just present, but validated)?
- What does it actually assert - full AI generation, minor edits, or something in between? Platforms differ in what they disclose.
- Does that assertion change what you thought you were looking at? Even an edit described as minor can change meaning; “AI-generated” on something you assumed was a photograph changes a lot.
- If there is no badge, move on to the source-check methods in AI image limits rather than treating the absence as a signal either way.
Why the standard itself is still spreading unevenly
C2PA adoption is opt-in, and implementations can support different operations: creating, validating, displaying, preserving, or recovering credentials. The current Content Credentials specification, C2PA explainer, trust model, and user-experience guidance describe those distinctions. NIST’s synthetic-content transparency report explains why transparency can contribute to trustworthiness without guaranteeing it. Apply source checks whether or not a badge is present.
Read a manifest without overreading it
Invented teaching display, not an inspected real file: validation says “valid”; signer is “Example Editing Service”; recorded action is “background replaced.” The supported conclusion is that the validated record attributes that action to that signer for this asset. It does not establish where the person was photographed, permission to depict them there, or the truth of a caption saying “at yesterday’s conference.” Save the actual assertions and check that caption separately. If your viewer cannot validate the file, record that limitation rather than upgrading “present” to “trusted.”