Start with one row per AI system and actual use. Record its supplier, purpose, data, affected people, decision impact and accountable owner. That is the evidence needed to assess the company’s role and obligations; buying an AI tool does not answer either question.
This guide prepares an SME for qualified classification and operational decisions. It does not determine that a system is compliant. The worked example below deliberately leaves legal questions open until the relevant facts and review are available.
The timeline that matters
The EU AI Act (Regulation (EU) 2024/1689, as amended by Regulation (EU) 2026/1744) applies in phases. The timetable below was checked on 28 September 2026 against the Commission’s AI Act page, AI Omnibus entry-into-force notice, and AI Act Service Desk enforcement FAQ. The Act entered into force on 1 August 2024. Prohibitions, definitions, and the then-applicable AI-literacy provisions started applying from 2 February 2025; governance and general-purpose AI model obligations became applicable on 2 August 2025. The AI Omnibus entered into force on 27 July 2026 and amended parts of the timetable and literacy framework. Article 50 transparency duties have applied since 2 August 2026. The Service Desk describes a limited transition to 2 December 2026 for providers of systems placed on the market before 2 August 2026 to meet the Article 50(2) marking and detection obligation.
The final AI Omnibus timeline has rules for systems used in certain high-risk areas such as biometrics, critical infrastructure, education, employment, migration, asylum, and border control applying from 2 December 2027, while high-risk systems embedded into regulated products apply from 2 August 2028. Because these dates have already shifted once, check the Commission page before committing budget to a compliance deadline.
What non-compliance actually costs
The penalty framework is one input, not a substitute for determining scope. The tiers below are based on the Commission Service Desk’s Article 99 text and require counsel to confirm how the amended framework and national rules apply:
- Prohibited practices under Article 5: up to €35 million or 7% of worldwide annual turnover, whichever is higher. The definitions and exceptions are detailed; labels such as “manipulation” or “biometrics” are not a complete legal classification.
- The operator and notified-body obligations listed in Article 99(4), including specified provider, deployer, and Article 50 transparency duties: up to €15 million or 3% of turnover. Do not treat this as a cap for every other AI Act obligation.
- Supplying incorrect, incomplete, or misleading information to authorities in reply to a request: up to €7.5 million or 1% of turnover.
Two SME-relevant provisions affect the framework: for SMEs and startups each cap applies as the lower of the fixed amount and the percentage, and authorities must apply the Regulation’s penalty factors and proportionality rules. Do not treat an informal label as proof that a practice is prohibited or permitted: stop any possible Article 5 use and obtain qualified classification. An inventory helps identify scope; it does not keep an organization out of it.
Who supervises this in Estonia
The Consumer Protection and Technical Regulatory Authority (TTJA) describes itself as an AI-system supervisory authority and says some product and high-risk-sector oversight is forthcoming. Its page was updated 10 September 2026 and checked again 28 September 2026. Its summary table gives a general 2 December 2026 transparency date, while the Commission’s Service Desk says Article 50 duties generally apply from 2 August 2026 and describes a narrower provider transition. Do not rely on the summary table alone to set a deadline. The exact authority and duties for a particular system still require qualified confirmation. For an Estonian SME, keep the system inventory and vendor evidence ready and check which Article 50 duties already apply, including whether the limited Article 50(2) transition applies.
Use those dates as planning inputs, not as a substitute for legal confirmation. The practical point for SMEs is simpler: start now, because inventory, ownership, documentation, and human oversight take time to build.
Provider, deployer, or buyer?
“Buyer” is a useful procurement label but not a substitute for an AI Act role. An SME can be a provider, deployer, importer, distributor, product manufacturer, authorized representative, or affected person depending on the facts. The simplified table below is triage only:
| Role | What it means | SME example | Practical duty |
|---|---|---|---|
| Buyer (informal) | You procure a tool with AI features | CRM assistant, meeting summarizer, coding assistant | Determine the actual legal role; perform vendor due diligence and set internal use rules |
| Deployer | You put an AI system into use in your business | Support triage, lead scoring, HR screening workflow | Oversight, monitoring, disclosure, records |
| Provider | You place an AI system on the market under your name | AI chatbot product, scoring API, industry tool | Product compliance, technical documentation, risk management |
An organization can hold more than one role. A company that buys a model API, wraps it in an industry-specific product, and sells it to customers may have provider and other operator roles. A company that uses a SaaS chatbot internally may be a deployer. Counsel must classify the actual system, substantial modifications, name/brand, purpose, and supply chain.
Do not guess this in a meeting. Put every AI system in an inventory and classify the role.
Build the AI inventory
Start with a spreadsheet. Every AI system gets one row:
| Field | Why it matters |
|---|---|
| System name | People need a shared label |
| Vendor or owner | Someone must answer questions |
| Business purpose | Risk depends on intended use |
| Users | Internal staff, customers, applicants, public |
| Data categories | Public, internal, personal, confidential, restricted |
| Output use | Draft, recommendation, automated decision, customer-facing answer |
| Human oversight | Who checks it and when |
| Disclosure | Whether people are told they are interacting with AI |
| Logs | What evidence exists after use |
| Classification questions | Possible Article 5, Annex I/III or Article 50 issue, with facts and review status |
Keep evidence and unresolved questions beside the label. A blank classification cell is not clearance.
Classify practical risk
Do not start by asking “is this high-risk under Annex III?” Start with operational impact:
Draft assistance. Editing or summarising for a reviewer may limit some output consequences, but the input can still contain restricted information. Assess purpose and data rather than assigning a low-risk legal category from the tool name.
Interaction and publication. Chatbots, voice agents, AI-generated media, public text or support responses. Disclosure and user clarity matter.
Decision-support workflows. Lead scoring, support routing, invoice handling, quality review, fraud flags. Human oversight, monitoring, and appeal paths matter.
Potential high-risk areas. Employment, education, credit, essential services, healthcare, law enforcement, migration, critical infrastructure, biometric categorization. Legal review required before deployment.
Possible prohibited practice: stop and escalate. Do not deploy a use that may fall within Article 5 while waiting for an internal “approval.” Qualified counsel must determine scope; an internal approval cannot make a prohibited practice lawful.
This is not a final legal classification. It is the triage that tells you where expert review is needed.
Minimum SME governance controls
For each non-trivial AI system, require six controls:
- Owner. One named person or team accountable for the system.
- Use boundary. What the system may and may not be used for.
- Data rule. What data can enter the system.
- Human oversight. Which outputs need review before action.
- Monitoring. How errors, complaints, drift, and vendor changes are noticed.
- Record. What evidence is kept: vendor docs, prompts, settings, approvals, logs, test results.
These controls address concrete failure modes: missing ownership, unknown data flows, ineffective oversight, and inability to reconstruct why an output was used. Their presence does not itself establish compliance or effectiveness; test and audit them.
Vendor due diligence
For vendor tools, ask for evidence rather than promises:
- Is customer data used for training by default?
- Where is data processed and stored?
- What retention controls exist?
- Are enterprise settings available for training opt-out, logging, SSO, and access control?
- Does the vendor provide AI Act, GDPR, security, and subprocessors documentation?
- Can the AI feature be disabled or scoped?
- Does the vendor disclose model providers and major architecture changes?
- What happens if the vendor changes model, prompt, or retrieval behavior?
If required evidence is missing, do not send the affected customer, employee or confidential data while the gap remains. A “low-risk” label does not repair an unknown data flow. Use public/synthetic preparation or a separately approved alternative.
Disclosure and human oversight
For customer-facing AI, disclosure should be simple and visible. If a customer is talking to an AI chatbot or voice agent, say so. For AI-assisted text, check applicable law, contract and policy together; internal policy cannot waive another obligation. Public-interest text has specific Article 50 qualifications. See the workplace disclosure decision guide.
Human oversight must be specific. “A human is in the loop” is not enough. Define:
- What output the human sees.
- What source evidence they can inspect.
- Whether they can override or reject.
- How much time they have.
- Whether approval is logged.
- What happens when the human disagrees with the system.
Oversight without authority is theatre. If the human cannot stop the action, they are not meaningful oversight.
A worked SME decision record
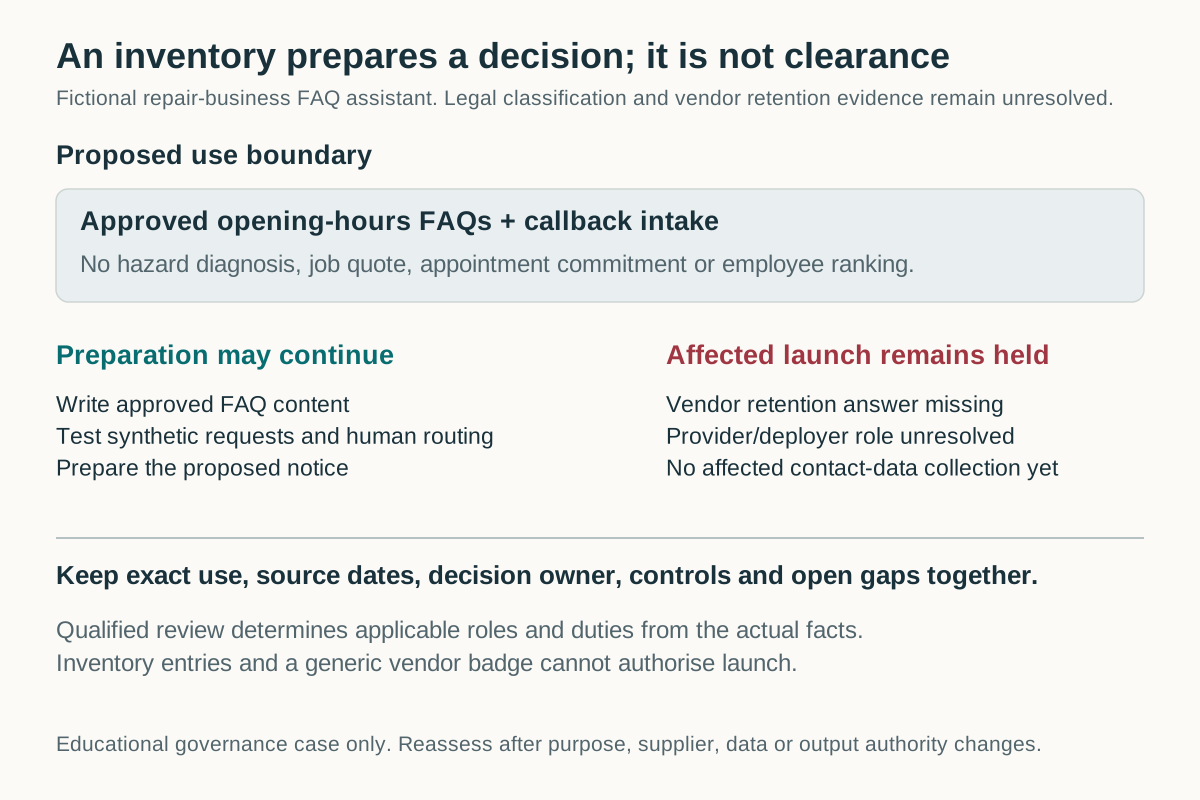
This fictional repair business wants a website assistant to answer opening-hours questions and collect callback requests. It does not diagnose hazards, quote jobs, rank employees or commit appointments.
| Record field | Initial entry | Evidence or unresolved decision |
|---|---|---|
| Purpose/output | Approved FAQ answers and callback intake | Test that a request for electrical repair instructions goes to the published human route |
| Data | Contact detail and customer-written request | Confirm necessity, notice, processor, access and retention before collecting it |
| Role | Business integrates a vendor model into its branded service | Qualified reviewer assesses provider/deployer facts; “we bought an API” is insufficient |
| Transparency | Direct public interaction | Record applicable notice/marking duties and exceptions, not just a generic vendor badge |
| Oversight | Named owner can disable intake and inspect approved evidence | Test access, stop behaviour and pending-request handling |
| Launch state | Preparation only | Vendor retention answer and legal role decision still missing |
The team can write the FAQ, test synthetic requests and prepare the notice while those questions remain open. It cannot claim the inventory itself authorised personal-data collection. A later expansion into appointment commitments or applicant screening triggers a new assessment.
Use an evidence sequence rather than a compliance calendar: inventory the use, resolve role and risk questions, establish controls, test them, then make the documented release decision. A month may be enough to assemble a baseline or may not; elapsed time does not establish compliance.
Keep the decision current
Use the SME governance checklist to retain the exact use, provision, source date, reviewer decision, controls and unresolved gaps. Revisit after a change in purpose, supplier, data, output authority or applicable rules. Where a national summary and Commission guidance differ, record the discrepancy and obtain a resolved deadline for the actual duty.