Connecting a model-driven workflow to email, calendars, CRM, project tools, or a knowledge base can remove manual transfers. It also exposes whatever the connector identity may read or change, subject to the provider’s real scope and the workflow’s controls.
This is also where things go wrong. An AI with access to your email can send embarrassing or expensive messages. An AI with calendar access can double-book you. An AI with CRM write access can corrupt customer records. The same connections that raise productivity create real risks.
This is an engineering risk guide and evaluation checklist. It cannot certify an integration as safe or compliant.
OWASP’s Excessive Agency guidance complements its prompt-injection guidance: minimize tool functionality, permissions, and autonomy, and require authorization outside the model for consequential actions.
Treat a tool connection as a grant of access. If an AI workflow can read private data or take an external action, it needs ownership, scope, approval rules, logging, and a rollback path before launch.
The three connection patterns
Three connection patterns you may encounter are:
1. MCP (Model Context Protocol). A protocol supported by multiple clients and servers. Compatibility does not make a server trusted: review its code, requested credentials, tool surface, transport, and deployment boundary before connecting it.
2. Native integrations. Some AI products document first-party or partner connectors. Availability, supported actions, data handling, and administrative controls vary by plan and can change; verify the live provider documentation for the exact tenant.
3. Workflow-platform tools (Zapier, Make, n8n). An automation platform can expose explicit triggers and actions. Its control and audit quality depend on the selected nodes, credentials, deployment, and workflow design.
Evaluate each pattern against the same requirements: supported operations, permission granularity, authentication, data path, approval UX, logs, failure handling, reversibility, and maintenance ownership. Protocol or product category alone does not determine the safest option.
Read before write
The single most important pattern: start with the minimum read scope. Add each write action only after its positive and negative acceptance tests pass. Elapsed time alone does not demonstrate reliability.
A read-only connection usually has lower integrity risk than a write connection, but it is not low-risk by default. It can expose private email, meeting subjects, attendee identities, customer records, or secrets; retrieved content can also carry indirect prompt injection. OWASP documents that external content can manipulate an agent toward sensitive-data disclosure or unauthorised functions (LLM01: Prompt Injection). Bound both what can be read and where model output can be sent.
A write-enabled workflow can send an unintended email, schedule the wrong attendees, or corrupt a CRM record. A good score on summarisation does not establish that action selection, recipient resolution, authorisation, and retries are safe.
So: start by giving the agent the minimum read access needed. Let it pull context, surface information, and draft responses. Manually review and execute writes. Promote a specific write action only after a representative evaluation, adversarial tests, approval and timeout tests, incident/rollback rehearsal, and an accountable owner accept the residual risk. Keep high-consequence actions gated regardless of a good average score.
This applies to every connection. Even when you do enable write access, do it action by action, not all at once.
Specific integrations and their risks
Read permission and write permission protect different things. A private calendar summary can leak attendees without changing an event. A CRM write can be technically valid yet update the wrong customer. A knowledge index can retain a page after its source access was revoked.
Before choosing a connector, inspect the actual provider scopes. Google Calendar’s scope reference, for example, distinguishes availability access from event-reading and event-writing scopes. If the task needs free/busy information, an event-content scope may disclose more than required. A connector’s friendly “calendar access” label is not a sufficient specification.
The application must also restrict the selected calendars, records and recipients. OAuth scope alone may be broader than the workflow’s business permission. When a connector cannot enforce the required boundary, use a narrower interface or leave the connection disabled.
Email sends, chat DMs and event invitations are external communications. Define who may receive them, what approval covers, and whether an approved policy permits bounded automatic messages. A blanket ban on every DM is less useful than a tested recipient and purpose boundary. Broad money-movement or deletion access requires a separate high-consequence design; it is outside this productivity example.
Build an integration risk register
Before granting tool access, write down the risk model in a table. This makes scope and stop conditions reviewable before a successful demo is mistaken for production evidence.
| Integration | Access | Allowed actions | Human gate | Log required | Stop condition |
|---|---|---|---|---|---|
| Calendar | Read + create events | Create confirmed meeting only | Approve before create | Proposed attendees, time, title, approver | Any event created with wrong attendee |
| CRM | Read + add note/task | Add an authorized note or follow-up task | Policy-defined review | Protected record reference, owner, source/version and result; avoid raw notes in general logs | Duplicate or wrong-contact update |
| Read + draft | Draft replies from approved templates | Human sends | Thread ID, draft ID, template version | Draft includes confidential internal detail |
For each integration, define five things:
- Permission scope. Exactly which account, folder, mailbox, workspace, or object type the agent can access.
- Allowed actions. The positive list, not a vague “can use CRM.”
- Human gate. Approve-before-act, act-with-window, or a documented low-risk review-after-act policy.
- Audit evidence. What must be logged to explain the action later.
- Stop condition. The signal that immediately pauses the workflow.
The companion risk-register template linked from this article gives you a reusable starting point.
Authentication and scoping
How you authorise the AI to act on your behalf matters as much as what you let it do.
Use scoped credentials, not shared personal logins. Where the provider supports API keys, OAuth scopes, service accounts, or workload identities, use the narrowest credential that can perform the approved action. Verify the actual provider scopes; a friendly permission label may still cover multiple resources.
Dedicated workload identities for automated agents. Use a service account, bot identity, or other provider-supported non-person identity where available, scoped to the workflow. Some consumer services do not support service accounts for the needed resource; do not bypass that limitation by sharing a personal login.
Refresh and rotate. Credentials can leak. Follow the provider’s supported rotation/revocation process and your organisation’s risk-based credential policy; do not invent a universal interval. Store refresh tokens as secrets and test revocation.
Audit and revoke. Periodically review which integrations have access to which accounts. Revoke anything you no longer use.
Don’t use personal credentials in shared agents. If your team is using an agent that has access to “Mary’s Gmail,” that is a fragile setup that breaks when Mary leaves and creates ambiguity about who is responsible for the agent’s actions. Choose a provider-supported identity and delegation arrangement approved for that mailbox; service accounts are not a universal substitute.
The human-in-the-loop patterns
For any non-trivial write action, a human-in-the-loop pattern is the right default. Three useful patterns:
Approve-before-act. The agent drafts the action and requires explicit human approval before executing. Friction is real but appropriate for high-stakes actions.
Act-with-window. The system queues the proposed effect and delays dispatch while a named reviewer can cancel it. Verify whether the provider has already exposed any data or invitation before the cancellation window ends. A delay with no available reviewer is not meaningful review.
Review-after-act. The agent acts and a human samples or reviews actions later. Use this only for bounded, reversible, low-consequence actions with monitoring and a stop condition. A second model is not an independent human approval.
The right pattern depends on reversibility, data sensitivity, error detectability, and consequence. Customer-facing email and refunds should begin approve-before-act; any later relaxation needs measured evidence, policy authority, and a tested recovery path. Regulated or high-consequence decisions remain with qualified humans.
Audit logging
Every consequential action should produce an audit event. Capture only fields you can protect and justify retaining:
- Timestamp.
- The agent that acted (in case you have multiple).
- The trigger that caused the action.
- The agent’s final rationale or decision summary. Do not store private chain-of-thought.
- The tool that was called and sanitised arguments or stable references; never copy secrets into logs.
- The result.
- Any errors or warnings.
Store logs somewhere durable with access controls, retention limits, tamper protection appropriate to the risk, and redaction of secrets or unnecessary personal data. Review them on a defined cadence and after alerts. Measure your own failure rate; no generic percentage is transferable across agents and tasks.
Logs can support security, accountability, and audit evidence, but retaining them can itself create privacy and security obligations. Map each field and retention period to the applicable control or legal basis; a log does not by itself establish GDPR, SOC 2, or ISO 27001 compliance.
A candidate architecture to evaluate
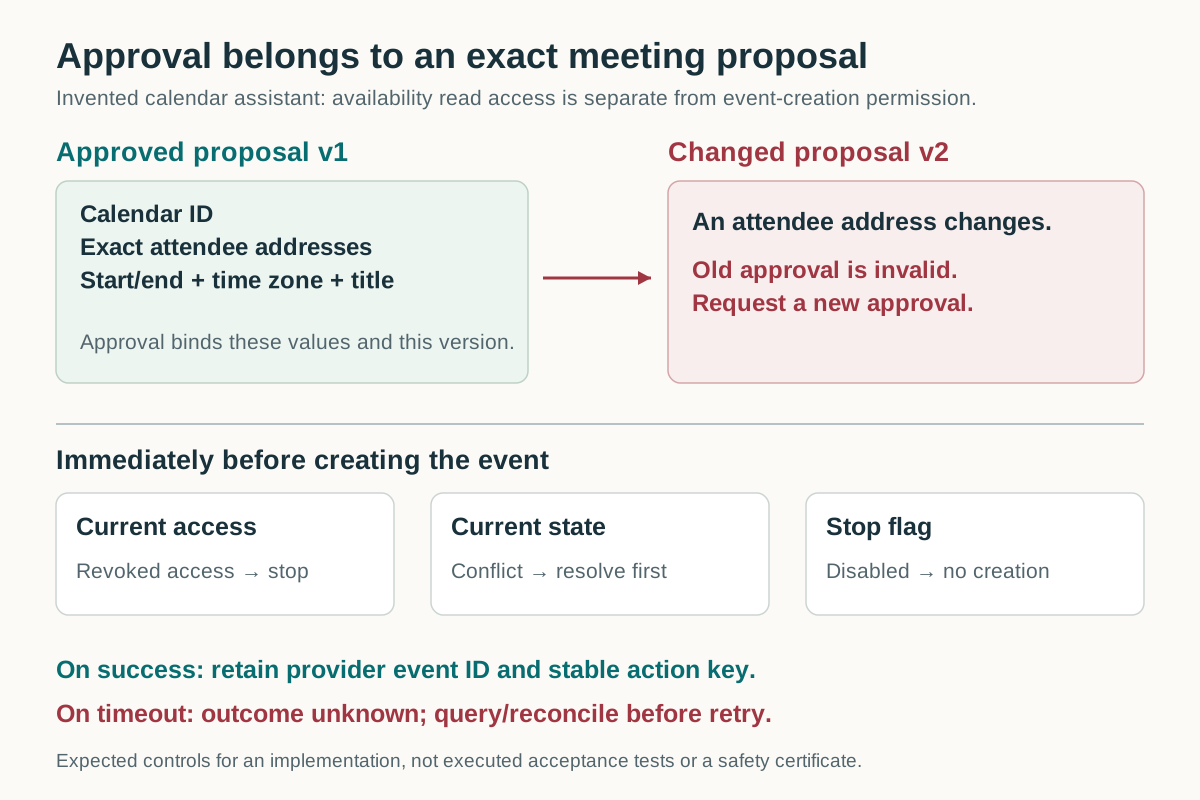
Consider an invented calendar assistant that proposes a meeting for two named colleagues. It first reads only approved availability, then prepares a proposal containing calendar ID, exact attendee addresses, start/end, time zone and title. The reviewer sees those fields before approval.
The execution service binds approval to the proposal version. If the model changes an attendee after approval, the old approval is invalid. Immediately before creating the event, the service rechecks current permission, calendar state and the stop flag. It records the provider event ID on success.
| Test | Required result |
|---|---|
| Two contacts share a display name | Ask for the intended address; do not guess |
| Attendee changes after approval | Require a new approval |
| Event creation times out | Mark outcome unknown; query/reconcile before retry |
| Same approved proposal is retried | One event, using a stable action key and provider reconciliation |
| Access revoked while a proposal waits | No creation on resume |
| Calendar text asks to forward private notes | No such tool or authorized recipient exists |
These are expected results for an implementation, not executed tests. A provider may lack the idempotency or lookup facility you need. Resolve that gap before enabling unattended retries.
Resolve the data-handling decision before launch
Write down the actual data flow: source account, connector operator, model provider, storage, logs and recipients. Ask the responsible privacy/security owner to approve the purpose, data classes, retention, processor arrangements and access boundary for that deployment. Specialist legal review may be needed for its jurisdiction or sector.
“Enterprise”, “local” and “read-only” do not settle those questions. Retain the approved decision with the connector record, and revisit it when a new feature adds a provider, tool or destination.
Test withdrawal as well as access
A useful integration record explains how to revoke credentials, pause new work and handle requests already admitted. Test a queued action after revocation and a timed-out action whose outcome is unknown. A switch that stops only new model calls may leave a dispatcher or already-running tool active.
Keep the tool inventory small, monitor errors and cost, and retire unused access. The risk register gives each grant a scope, owner, acceptance evidence and withdrawal path.